Most breaches that make headlines don’t start with a sophisticated zero-day exploit — they start with a stolen or misused privileged credential. A domain admin password sitting in a spreadsheet, a shared root password nobody’s rotated in years, a service account with far more access than it actually needs. Privileged Access Management (PAM) exists specifically to close that gap, and CyberArk is one of the most established names in the space.
What PAM Actually Does
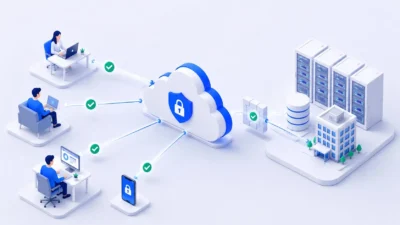
Privileged accounts — domain admins, database root users, network device credentials, service accounts — have the keys to everything. A PAM platform like CyberArk vaults those credentials centrally, rotates them automatically, and brokers access so that no human (or script) ever actually holds the plaintext password. Every privileged session is logged and, depending on configuration, recorded — turning “who touched this server and when” from a guessing game into an audit trail.
Why This Matters More Than It Used To
As IT environments in Hyderabad’s manufacturing and pharma sectors grow more complex — mixing on-prem servers, cloud infrastructure, and third-party vendor access — the number of privileged accounts multiplies quietly. Contractors get temporary admin access that’s never revoked. Legacy service accounts outlive the projects they were created for. Each one is a standing risk, and traditional IT teams often don’t have visibility into how many privileged accounts even exist across the environment.
Signs Your Business Needs PAM
- Privileged passwords are shared across a team via chat, email, or a spreadsheet.
- You can’t produce a clean answer to “who has admin access to what” without manually checking each system.
- Vendors or contractors are given standing (rather than time-boxed) access to critical systems.
- You’re pursuing a compliance certification (ISO 27001, SOC 2, or similar) that requires demonstrable access controls.
What a CyberArk Deployment Involves
A phased rollout works better than trying to vault everything on day one. Most successful deployments start with the highest-risk accounts — domain admins and database root accounts — get those vaulted and rotating, then expand to service accounts and third-party vendor access. Session recording and just-in-time access (granting privileged access only for the duration it’s actually needed) are usually added once the core vaulting is stable.
How MetaPoint Can Help
MetaPoint scopes and deploys CyberArk PAM for enterprises across Hyderabad, Telangana, Andhra Pradesh, and Karnataka, starting with a privileged-account discovery exercise to show you exactly what’s currently unmanaged. Contact us to start with an access audit.